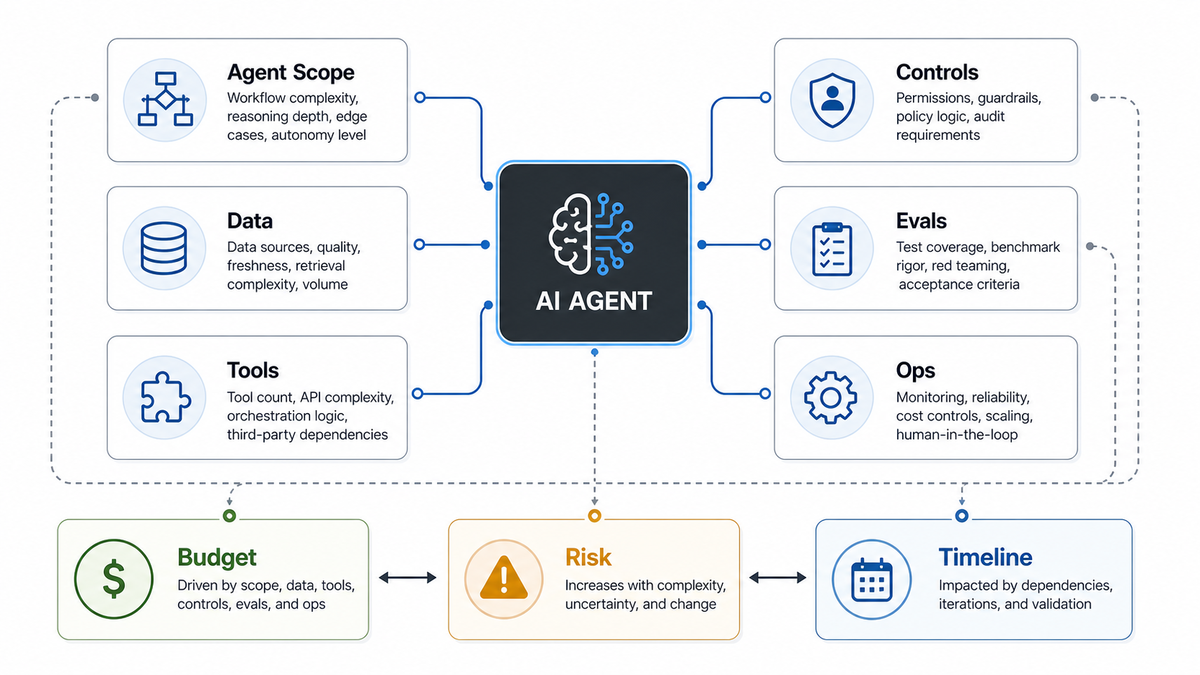
Secure AI Agent Development: OWASP Controls, Tool Permissions, and Audit Logs
Turn OWASP agentic AI risks into a secure AI agent development checklist for goals, tool permissions, approvals, memory, logs, and monitoring.
Check software quality, accessibility, release gates and security boundaries before launch.
Check software quality, accessibility, release gates and security boundaries before launch.
Start with the selected guides, then browse the complete collection by decision type. The directory includes older published articles as well as recent additions; use the archive below for search and chronological browsing.
Showing 37–37 of 37 posts
Turn OWASP agentic AI risks into a secure AI agent development checklist for goals, tool permissions, approvals, memory, logs, and monitoring.