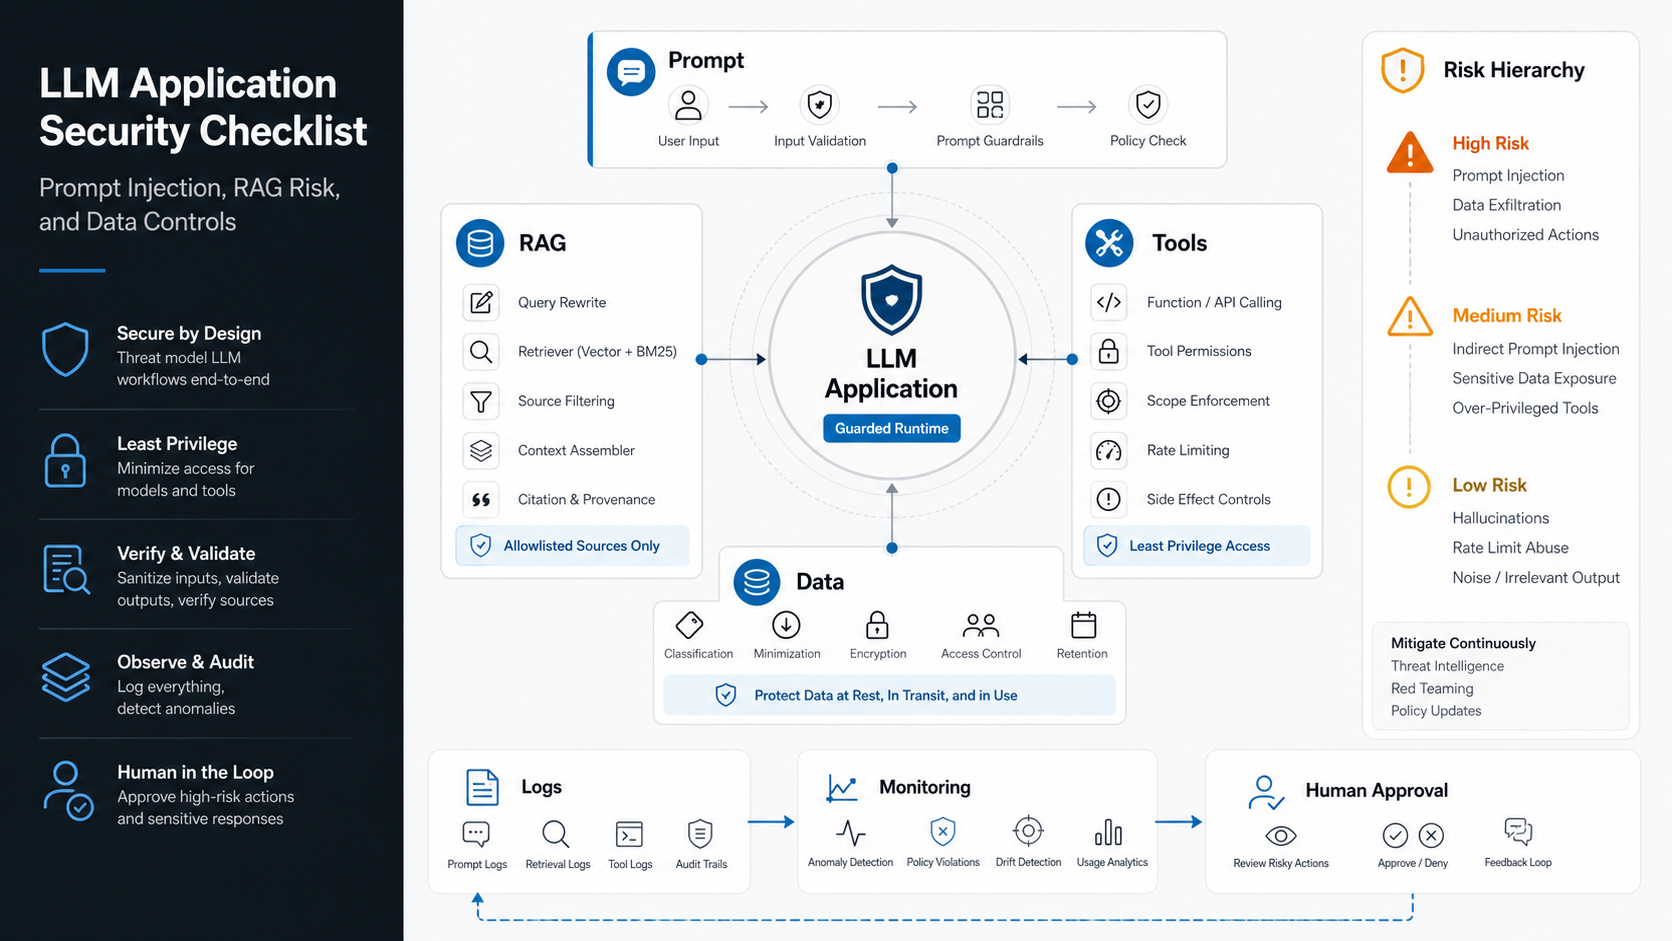
LLM Application Security Checklist: Prompt Injection, RAG Risk, and Data Controls
Use this OWASP-aligned LLM application security checklist to control prompt injection, RAG exposure, tool permissions, output handling, logs, and launch governance.
Explore RAG data preparation, retrieval quality, permissions, evaluation and production architecture.
Retrieval-augmented generation supplies a model with relevant material from a controlled source collection. It can support grounded answers, but retrieval quality and source permissions determine what the model can reliably use.
Evaluate document freshness, chunking, search relevance and citation accuracy separately from answer fluency. Test inaccessible documents, missing evidence and conflicting sources explicitly.
The guides below cover practical implementation choices. Begin with a measurable question set and an accountable content owner before expanding the corpus.
Showing 13–15 of 15 posts
Use this OWASP-aligned LLM application security checklist to control prompt injection, RAG exposure, tool permissions, output handling, logs, and launch governance.
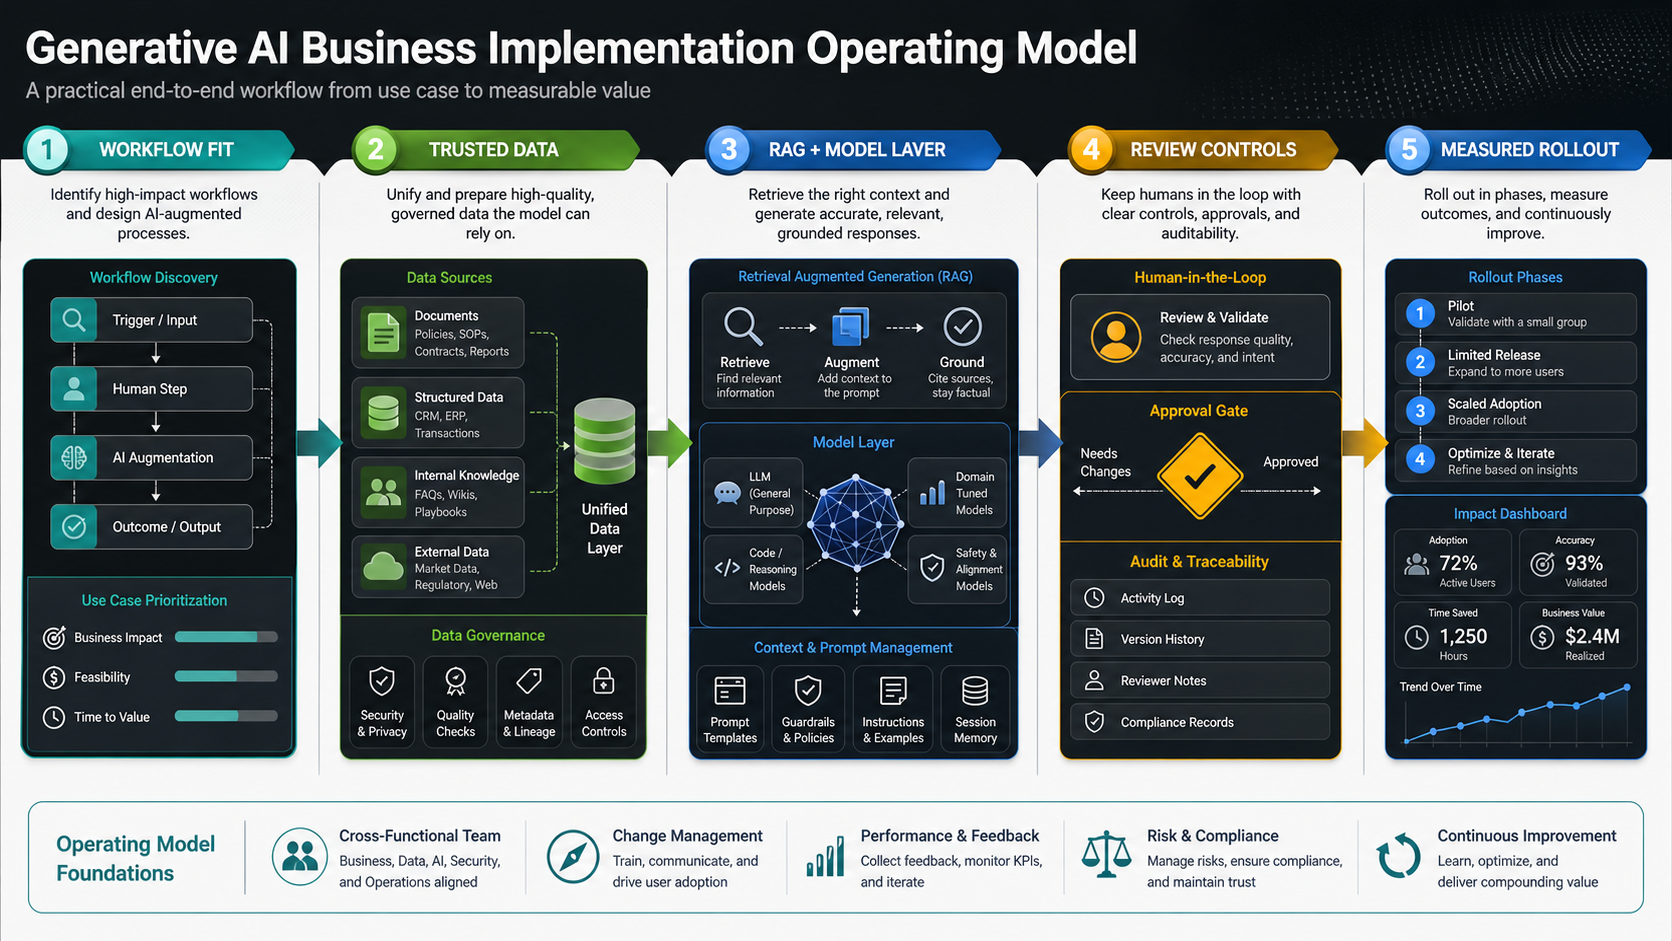
Plan generative AI for business with practical use cases, RAG architecture, governance controls, evaluation methods, ROI metrics, and rollout guidance.
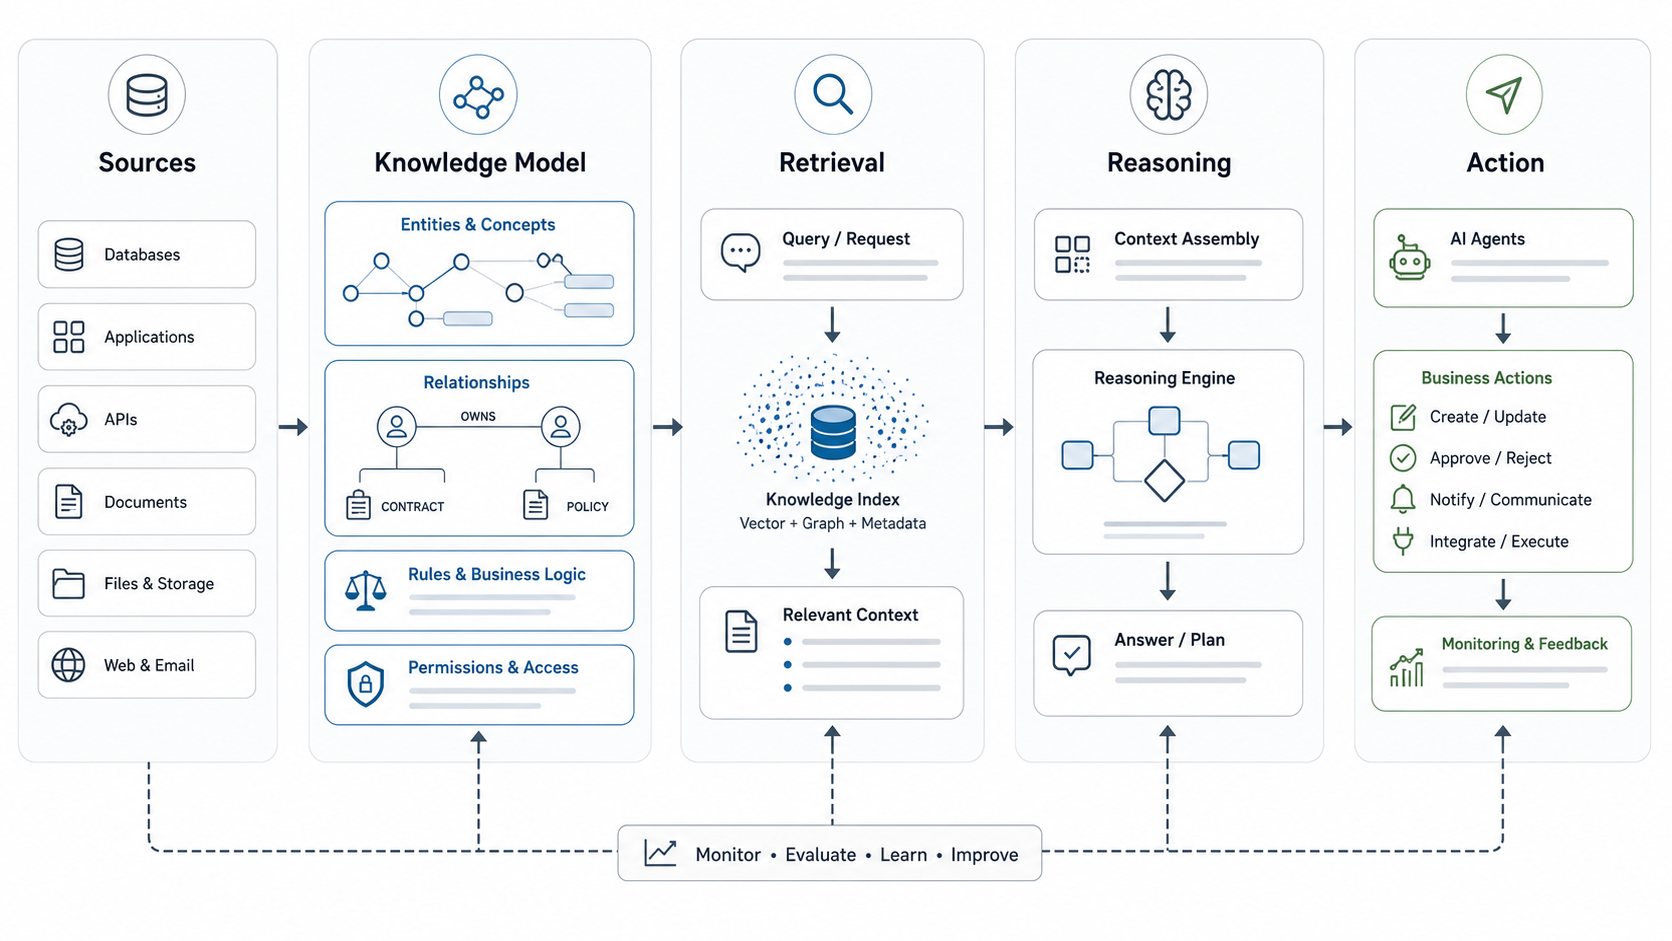
Learn how knowledge representation turns business data, rules, permissions, and relationships into reliable context for RAG systems, AI agents, and governed automation.